Challenge
Certificate lifecycle management and client authentication affect both service availability and access control. The work covered certificate rotation and systems using mutual TLS (mTLS), secure WebSockets (WSS), and JWT-based authentication.
TLS certificates establish transport trust for mTLS and WSS. JWT signing and verification use cryptographic keys and are a separate authentication concern; they should not be treated as the same lifecycle as transport certificates.
My contribution
I implemented certificate management with AppViewX on ECS Fargate and automated certificate rotation. Related certificate-proxy infrastructure used Terraform to provision an NGINX Plus platform for application access.
System overview
AppViewX provided the certificate-management capability. The related proxy architecture used NGINX Plus behind a network load balancer, with an EC2 Auto Scaling group, shared EFS storage, and CloudWatch integration. Its documented capabilities included LDAP integration, mTLS, issuer validation, and Grafana dashboards.
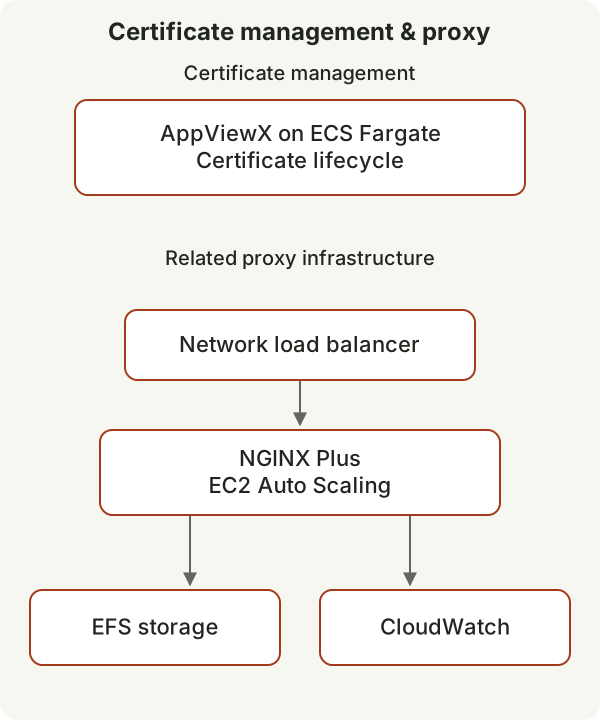
Text description: AppViewX runs on ECS Fargate for certificate lifecycle management. Separately, a network load balancer routes traffic to an NGINX Plus Auto Scaling group with shared EFS storage and CloudWatch integration.
Outcomes
Automated certificate rotation and supported a repeatable certificate-proxy infrastructure design for application access.
Engineering considerations
Certificate issuance, distribution, and application reload behavior all matter to a successful rotation. Trust validation must remain consistent as proxy instances change. Transport certificate rotation and JWT signing-key changes also need separate validation because their consumers and failure modes differ.
Supporting examples
Related learning material covering infrastructure security and deployment authentication: